Your Partner in
Cybersecurity, Data Protection
& Regulatory Governance

Helping Malaysian organisations strengthen cybersecurity, protect personal data and meet regulatory requirements, through training, consultancy and managed services scoped to their regulatory and operational needs.

Join our PDPA Awareness & Data Protection Officer (DPO)
Training Programme

Updated With 2024 Amendment & 2026 JPDP Guidelines

HRD Corp SBL-Khas Claimable

AML/CFT, Cybersecurity Awareness Trainings, Compliance Officer on Demand, CISO on Demand & Phishing Simulation Available
Send Us a Message

Our team will respond promptly to your inquiries.

Strengthening Cybersecurity, Data Protection & Regulatory Governance

From security risk to regulatory obligations, practical support across your compliance lifecycle
Professional working on a laptop, representing cybersecurity services

Cybersecurity

Protect your organisation from threats with proactive defence strategies
Professional working on a laptop, representing data protection services

Data Protection

Safeguard personal data and meet compliance obligations with confidence
Professional working on a laptop, representing regulatory and governance services

Regulatory & Governance

Strengthen your governance framework and regulatory compliance posture
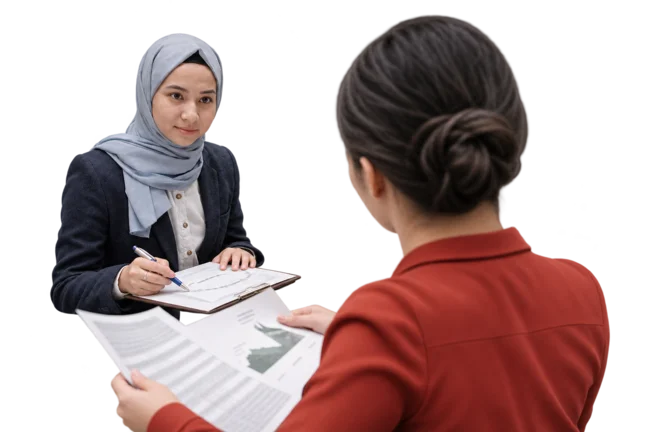
Two professionals reviewing a report together

Managed Services

Augment your team with expert support and ongoing compliance management
Professional representing assessments and advisory

Assessments & Advisory

Identify risks, close gaps, and strengthen your compliance and security posture

Training, Consultancy & Managed Services, across Cybersecurity, Data Protection and Regulatory & Governance

How Orbix Closes the Gap

Your compliance challenges and the outcomes Orbix delivers Six cybersecurity, data protection and regulatory challenges flow into Orbix, which maps them to six outcomes on the right Your Challenges Outcomes Orbix One Partner. Complete Compliance. Rising phishing &cyberattack risk No incidentresponse plan No DPO appointedunder PDPA No privacy policiesor notices AML/CFT & regulatoryaudit gaps No whistleblowingchannel Stronger security postureacross the organisation Confidence to respond to andrecover from any incident Full PDPA compliance, backedby qualified oversight Documentation that standsup to regulatory audit Audit-ready across everyregulatory requirement A governance frameworkregulators and boards trust Hover any item to learn more

How We Work

From assessment to ongoing support, here's how we help Malaysian organisations across cybersecurity, data protection and regulatory compliance. Start wherever you are, most clients begin with a single training or assessment.

01
Compliance Assessment & Data Mapping

Security, data protection and regulatory gap analysis across your organisation

02
Consultancy & Programme Design

Policy development, governance frameworks and compliance programmes tailored to your obligations

03
Training & Capability Building

Cybersecurity, regulatory and compliance training for your teams, in-house, online or self-paced

04
Managed Services & Ongoing Support

Phishing simulation, whistleblowing channel management, e-learning platform and ongoing DPO or compliance officer support

Professional waving hello on a video call during an online training session
Corporate team meeting during a compliance and training review session in Malaysia

Organisations Served Across Our Group
Frequently Asked Questions

Answers on cybersecurity assessments, PDPA and DPO compliance, AML/CFT and regulatory training, whistleblowing and governance services, and HRD Corp claimable training for Malaysian organisations.

Yes, as long as the course is delivered by an HRD Corp registered training provider and your company contributes to the HRD Corp levy. Registered employers claim the training fee back against their levy balance, which for most companies makes compliance and cybersecurity training close to cost-neutral. See the HRD Corp claimable training programmes available.

Both options work. In-house training brings the trainer to your office and suits teams of ten or more, because the scenarios can be built around your own systems, policies, and industry. Live online sessions work better for distributed teams and multiple branches. Larger organisations often combine the two with a self-paced corporate e-learning platform for annual refreshers.

Yes. Through the Orbix LMS and e-learning platform, staff complete awareness modules on their own schedule and device rather than attending one fixed session, which suits shift workers, multiple branches, or teams that can never all be in the same room on the same day. Each participant still sits a knowledge assessment and receives a verifiable certificate on completion, with reporting to HR at department level.

Yes, a Certificate of Completion is issued to every participant with full attendance, and each certificate can be verified online by an employer or auditor. Programmes with a practical component also include take-home toolkits such as breach response checklists, ROPA templates, and DPIA trigger checklists that staff can apply at work straight away.

Yes. AI Governance and Ethics covers AI risk, accountability and policy for organisations adopting AI tools, and the AI Governance Advisory service helps build an AI inventory and practical internal controls. Training on using specific tools safely, such as ChatGPT and Claude for Business, is covered separately under corporate training.

Yes. Our cybersecurity training and readiness assessments are updated for the Cyber Security Act 2024 (Act 854) and NACSA requirements, which matter most for organisations designated as National Critical Information Infrastructure (NCII) entities and their suppliers. See Cyber Security Act & NCII readiness.

Appointing a DPO is mandatory for any organisation processing the personal data of more than 20,000 individuals, sensitive personal data of more than 10,000 individuals, or carrying out regular and systematic monitoring of personal data. The duty applies to both data controllers and data processors. PDPA and DPO training prepares the appointed officer for the role.

Outsourcing suits organisations without in-house privacy expertise, since it gives access to a trained officer without the cost of a full-time hire and avoids the gap that opens up when that person resigns. An in-house DPO makes sense once data processing is heavy enough to need daily attention. Many companies start with an outsourced DPO service and build internal capability alongside it.

Compliance Officer as a Service supports the compliance officer your organisation appoints, with the sector, regulator and engagement responsibilities confirmed before work starts, rather than putting someone in that seat on your behalf. An in-house compliance officer carries the role full-time and still needs the same groundwork. Which fits depends on whether you already have someone to appoint and how much ongoing specialist support that person needs.

The three cover different accountabilities. CISO as a Service sets cybersecurity priorities and reports on security posture to management. Compliance Officer as a Service supports the officer appointed for a specific regulatory framework such as AML/CFT. DPO as a Service covers PDPA and data protection governance specifically. Many organisations need only one of the three; some regulated sectors need two or all three at once.

Once a year is the minimum. Organisations handling sensitive personal data, financial transactions, or high staff turnover do better with quarterly refreshers or phishing simulations run between the full sessions. Regulators, auditors, and cyber insurers increasingly ask for evidence of ongoing staff training rather than a single certificate from two years ago.

Yes. Islamic Finance and Shariah Governance covers Bank Negara Malaysia's Shariah Governance Framework: Shariah committee requirements, the product approval process and handling Shariah non-compliance risk, for Islamic banks, takaful operators and Islamic fund managers.

Yes. Trade Sanctions and Export Control covers Strategic Trade Act obligations: classifying controlled goods, permits and end-user screening. This is a different regime from AML/CFT targeted financial sanctions screening, which Orbix covers separately. An independent compliance review of the same scope is also available.

Beyond PDPA, Orbix covers AML/CFT for banking, capital markets and other reporting institutions, BNM Risk Management in Technology (RMiT), Securities Commission technology risk guidelines for capital markets, ISO 37301 compliance management systems and ISO 37001 anti-bribery management. See AML/CFT compliance, BNM RMiT training and Integrity & Governance solutions.

Yes. Orbix operates an independent, managed whistleblowing channel on your behalf, with web, email and phone reporting in English and Bahasa Malaysia, anonymous reporting, and case triage with a full audit trail. It supports the adequate procedures a company relies on under Section 17A of the MACC Act, ISO 37001 and the Malaysian Code on Corporate Governance. See Whistleblowing Channel Service.

A one-off training addresses a single requirement, such as an awareness session or a certification course. A managed service is ongoing: DPO-as-a-Service and Compliance Officer-as-a-Service provide continuous regulatory oversight, while phishing simulation and the whistleblowing channel run as standing programmes rather than single events. See DPO-as-a-Service and Compliance Officer-as-a-Service.

How Can We Help?